Transparency Note: This article was written and edited by me — a real human being — with light assistance from AI-based editorial tools for grammar and structural clarity. All examples, data, and contextual insights were authored and verified by me. AI tools were not used to generate financial, technical, or compliance assertions. This disclosure is included for compliance with Medium transparency standards.
In March 2026, Andrej Karpathy ran 700 ML experiments in 48 hours. One GPU. One objective metric. Clear constraints on what the agent could and couldn't touch. Twenty optimisations discovered. Eleven percent training speedup confirmed on larger models.
The system is called Autoresearch. It maps almost exactly onto the compliance challenge every regulated financial institution is already trying to solve.
The Experiment
Three components. That is all Autoresearch needs.
- An agent with file access — capable of modifying a single training file
- An objective metric — a clearly testable measure of success
- Time limits — fixed durations for each experimental run
The agent doesn't optimise freely. It reads research, forms hypotheses, runs experiments, and keeps only what improves the metric without violating the rules. What it must not change is defined upfront. The stopping criteria are set before the first experiment runs.
That design choice is the point. Constraints are embedded. They are not a review layer tacked on after the agent has done its work.
The Finance Parallel
Image produced by Gemini-2.5-Flash
Every AI deployment in financial services already runs a version of this framework — whether the teams running it recognise it or not.
The objective metric: portfolio returns, fraud detection rates, customer satisfaction scores, processing speed.
The constraints: regulatory requirements, risk limits, explainability mandates, data sovereignty rules, audit trail obligations.
The time limits: regulatory reporting deadlines, real-time transaction monitoring windows, model validation cycles.
Here is where it diverges. In Karpathy's world, a failed experiment costs five minutes of GPU time. In finance, a constraint violation can mean regulatory action, client losses, or reputational damage measured in millions.
Yet most financial AI systems are not built constraint-first. They are built to optimise first, then bolted onto compliance frameworks after the fact. That gap — between how AI is designed and how it is governed — is exactly what regulators are now scrutinising.
Why Rules-Based Compliance Is Hitting a Wall
Traditional compliance automation runs on a deterministic model: if condition A, then action B. Reliable, auditable, and increasingly inadequate.
The failure mode is structural. Rules-based systems generate large false-positive volumes because any data deviation triggers manual review. They break under messy inputs — misspellings, conflicting records, unstructured narratives. When regulations change or new risk patterns emerge, someone has to manually rewrite the rules.
Financial institutions using rules-based AML screening find compliance teams drowning in alerts. In practice, the majority of analyst time goes to investigating false positives rather than actual threats. That is not a resource problem. It is a design problem.
Agentic AI approaches this differently. Rather than executing fixed rules, these systems reason through compliance objectives dynamically. They handle linguistic variation, semantic context, and behavioural patterns. Fewer false positives. Better performance on messy, contradictory data — the kind of data financial institutions actually have.
But this flexibility creates its own risk. An unconstrained agent optimising for alert reduction might learn to suppress genuine threats. An agent optimising trading returns might drift into strategies that violate position limits or concentration rules.
That is the core tension. And it is exactly what the Autoresearch architecture addresses.
The Constraint-Based Architecture Finance Needs
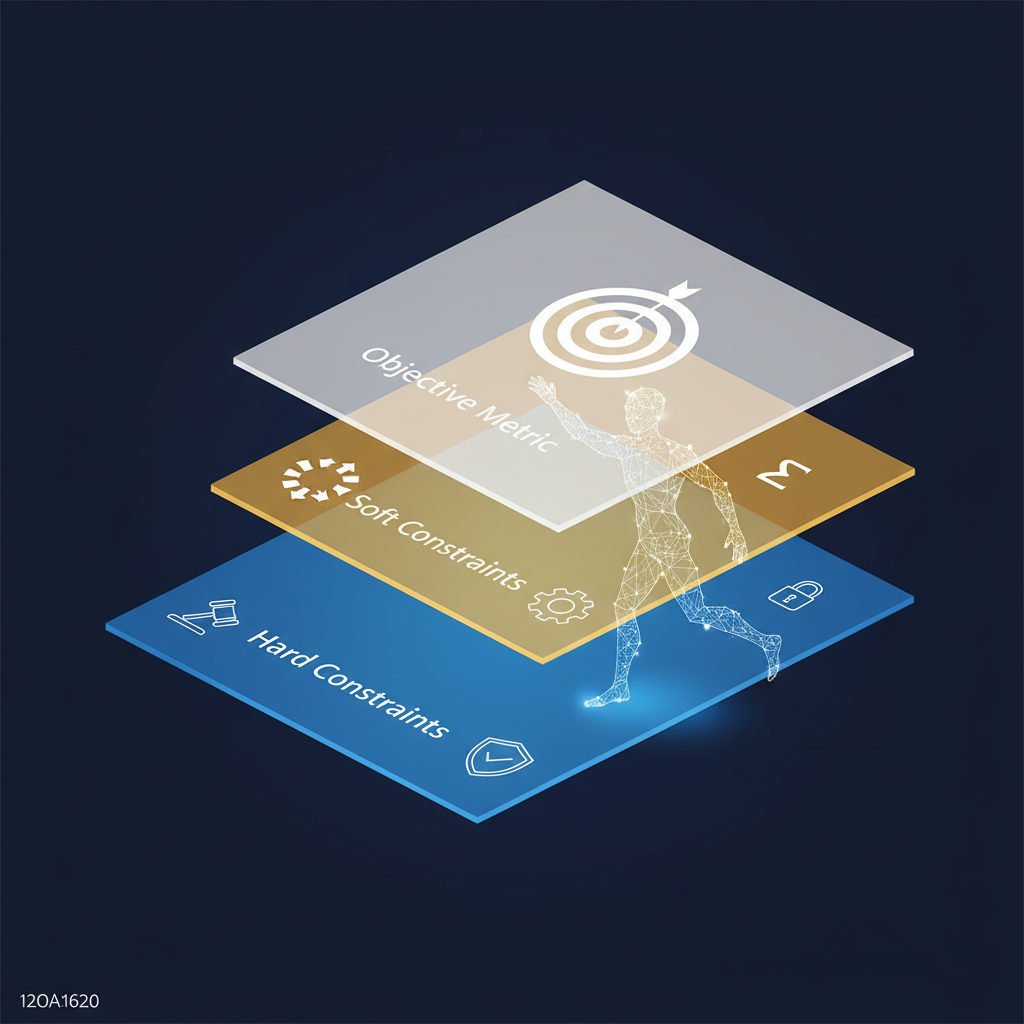
Hard constraints, soft constraints, objective metric — the three layers of constraint-based AI architecture. Image produced by Gemini-2.5-Flash
The Autoresearch pattern points to a different model: embed constraints at the architecture level, not the review layer.
Hard Constraints: The Non-Negotiables
These are the equivalent of Karpathy's "what shouldn't change" directives.
Regulatory boundaries
Position limits, capital requirements, reporting obligations. The agent cannot modify, circumvent, or optimise away these parameters.
Explainability requirements
Every decision must generate a transparent reasoning chain — not as a post-hoc justification, but as an intrinsic part of the decision process.
Data sovereignty
Sensitive data stays within defined boundaries. Small Language Models deployed within institutional cloud environments deliver AI capability without routing client data to external providers.
Human escalation triggers
Defined thresholds where the agent must stop and defer to human judgement. Not optional. Not configurable by the agent itself.
Soft Constraints: The Optimisation Space
Within the hard boundaries, the agent has room to experiment:
- Which data sources to weight more heavily in risk assessment
- How to sequence compliance checks for maximum efficiency
- What patterns to flag for human review versus auto-resolve
- How to allocate processing resources across monitoring tasks
The agent can modify the training file. It cannot modify the objective metric or the stopping criteria.
The Objective Metric
This is where most financial AI implementations go wrong. They optimise for a proxy metric — alert volume, processing speed — rather than the actual objective: accurate risk detection, regulatory compliance.
Proxy metrics produce proxy compliance. The Autoresearch model demands a single, clear metric. In financial compliance, that metric needs to capture both performance and constraint adherence simultaneously.
Multi-Agent Coordination: The 2026 Reality
The industry is moving toward multi-agent architectures for compliance. For good reason.
One agent analyses transaction patterns. Another interprets current regulations. A third assesses risk. A fourth evaluates customer behaviour. Together they synthesise conclusions that no single model could produce reliably.
Karpathy's framing: "You spin up a swarm of agents, you have them collaborate to tune smaller models, you promote the most promising ideas to increasingly larger scales." In a compliance context:
Regulatory scanning agents continuously monitoring global regulatory sources, mapping new obligations to internal policies
Transaction monitoring agents applying constraint-aware pattern detection across real-time data
Risk assessment agents evaluating portfolio-level exposure against dynamic limits
Audit agents generating compliance documentation as a byproduct of normal operations, not a separate workstream
The design principle is the same whether you are training ML models or governing financial AI: constraints must be embedded, not appended.
From Periodic Review to Continuous Constraint Satisfaction
The shift from rules-based to constraint-based AI in finance mirrors a broader regulatory shift. Outcome-based oversight is replacing checkbox compliance.
Regulators are increasingly defining expected results rather than mandating specific procedures. This rewards institutional innovation while maintaining consumer protection standards. Firms that build constraint-aware systems — systems that demonstrate continuous compliance rather than point-in-time adherence — will have a structural advantage.
The EU AI Act, fully applicable from August 2026, classifies many financial AI applications as high-risk: credit scoring, insurance pricing, fraud detection. All require stringent documentation and ongoing monitoring. Constraint-based architectures naturally produce that documentation trail, because the constraints and their satisfaction are intrinsic to how the system operates. You are not generating compliance reports separately. The compliance record is a byproduct of the system doing its job.
That is a significant efficiency gain. And it is a design choice, not something you retrofit later.
What to Build
For financial institutions evaluating AI systems today, the Autoresearch model offers a practical design checklist:
Define hard constraints before any optimisation work begins
What are the non-negotiable boundaries? Write them down before you write a line of code.
Establish a single, clear objective metric
One that captures both performance and compliance. If you cannot measure it, the agent cannot optimise for it.
Build constraint checking into the loop
Not as post-hoc review, but as a gate every iteration must pass through.
Set explicit stopping criteria
Conditions under which the system halts and reports rather than continuing to iterate.
Maintain human oversight at the boundary
Where hard constraints meet edge cases that require judgement, not automation.
The firms that will lead in regulated AI are not the ones deploying the most powerful models. They are the ones building the most intelligent constraint architectures.
The gap between "AI that works" and "AI that works within regulations" is a design problem, not a performance problem. Build the constraints in. Optimise inside them.
Author's Bio
Terry Yodaiken advises investment and wealth managers on AI adoption, hybrid data architectures, and explainable decision systems. POVIEW.AI helps institutions build governed, production-grade AI that delivers measurable commercial outcomes.